DPDP compliance for higher education is no longer a question of whether a university has a privacy policy. It is a question of whether the institution can prove, on any given day, what personal data it holds, why it holds it, who can see it and when it will be deleted.
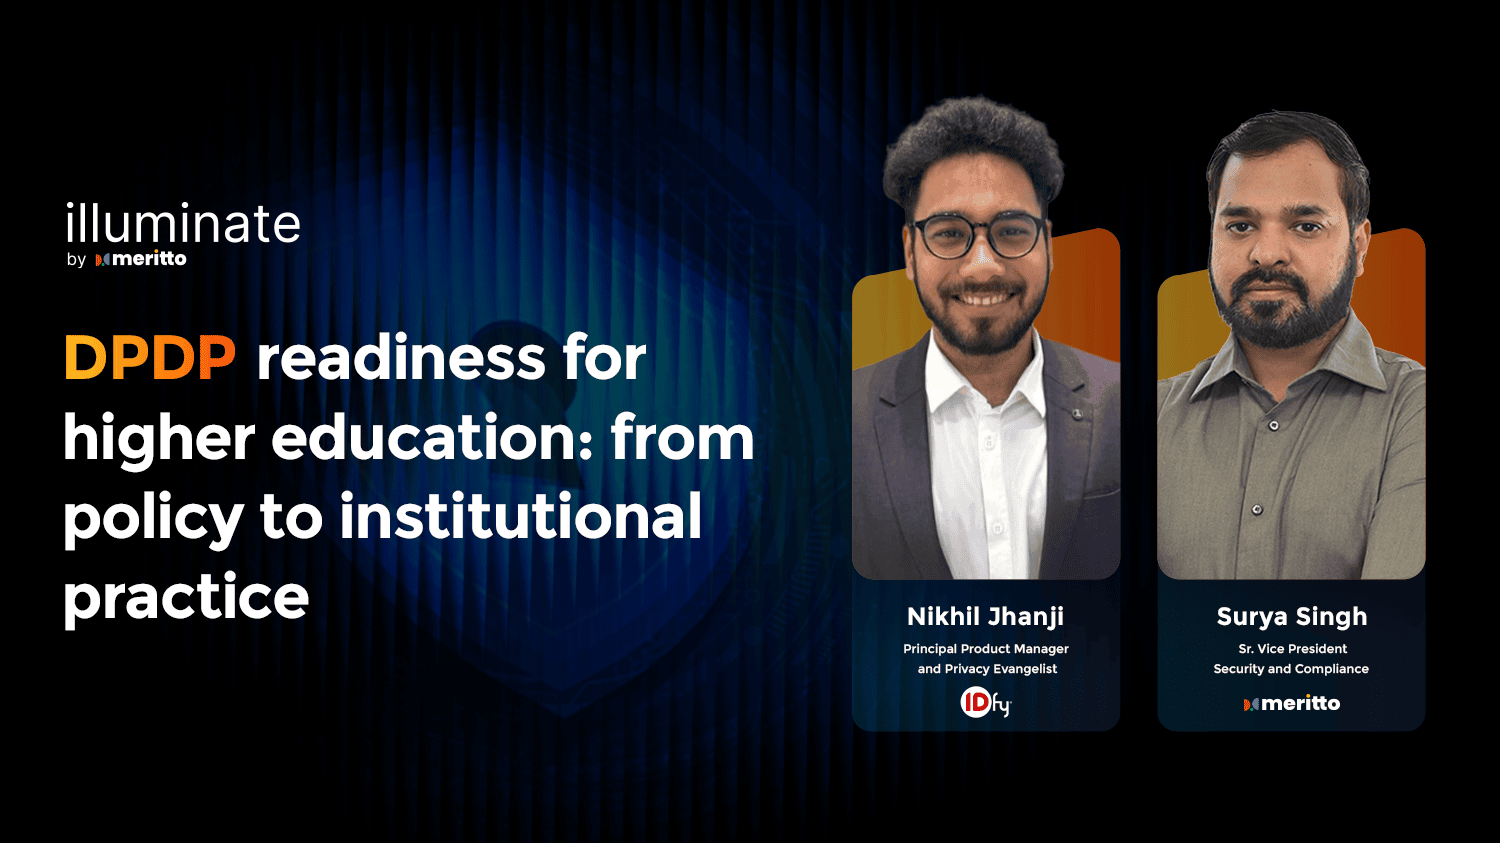
That shift, was the center of our recent #illuminateByMeritto webinar, “DPDP readiness for higher education: from policy to institutional practice.” Nikhil Jhanji, Principal Product Manager and Privacy Evangelist at IDfy, and Surya Singh, Senior Vice President, Security and Compliance at Meritto, walked through what the Digital Personal Data Protection Act, 2023 and the DPDP Rules, 2025 ask of universities and colleges, and how an institution turns each obligation into something it can demonstrate.
What is the DPDP Act, and why does it matter to universities?
The Digital Personal Data Protection Act, 2023 (DPDP Act) is India’s law governing how organizations process digital personal data. The DPDP Rules, 2025, notified by the Ministry of Electronics and Information Technology on 13 November 2025, set out how the Act works in practice. Together they define who is responsible for personal data, what individuals can ask for and what happens when things go wrong.
Few organizations hold personal data as broadly as a university. A single student generates records across admissions, academics, hostel, finance, placements and campus security, often over many years. Much of this data does not look personal at first glance, yet it carries an identifier that links it to a person.
| Institutional activity | Personal data it typically contains |
| Application form submissions | Name, mobile number, email ID |
| Entrance exam scores | Roll number, application ID linked to an individual |
| Attendance records | Student ID, biometric attendance |
| LMS usage logs | Login credentials, IP address, device identifiers |
| Hostel allocation | Room number linked to student identity |
| CCTV footage | Facial images, movement patterns |
| Fee payment records | Bank account number, UPI ID |
| Scholarship details | Income certificates, caste or category data |
| Placement resumes | Educational history, contact details |
| HR records | Aadhaar, PAN, salary details, biometrics |
The point the session made is simple: once data becomes identifiable, the obligations around notice, consent, purpose limitation, retention, security and erasure apply automatically. There is no separate category of “routine” institutional data that sits outside the law.
Who is who under DPDP on a campus?
The DPDP Act assigns every party a role, and each role carries different duties. In a university setting, the roles map as follows.
| DPDP role | Definition | Campus example |
| Data Principal | The individual to whom the personal data relates. For a child, this includes the parent or lawful guardian. | Applicant, student, parent, staff member. |
| Data Fiduciary | The entity that decides the purpose and means of processing. It is fully accountable for compliance. | The university or college. |
| Data Processor | An entity that processes personal data on behalf of a Data Fiduciary. | CRM, LMS, ERP and payment platforms |
| Consent Manager | An entity registered with the Data Protection Board that lets a Data Principal give, manage, review and withdraw consent through one platform. | A registered consent platform the student uses |
| Significant Data Fiduciary | A Data Fiduciary notified by the Central Government based on factors such as the volume and sensitivity of personal data it processes and the risk to the rights of Data Principals. Under Section 10 and Rule 13, it must appoint a Data Protection Officer based in India, appoint an independent data auditor, and conduct a Data Protection Impact Assessment and an audit once every twelve months. | Applies only if the government notifies the institution or class |
A university remains accountable for compliance even when a vendor does the processing. Section 8(1) of the Act is explicit on this, which is why vendor governance appears later in this guide as a core proof, not an afterthought.
What is the DPDP compliance deadline for universities?
The DPDP Rules, 2025 come into force in three phases. Most obligations that touch day-to-day university operations apply from May 2027, eighteen months after the Rules were notified.
| Date | Milestone | Status |
| August 2023 | DPDP Act receives assent | Behind you |
| January 2025 | Draft DPDP Rules published for consultation | Behind you |
| November 2025 | Rules notified. Data Protection Board framework takes effect (Rules 1, 2 and 17 to 21) | Behind you |
| November 2026 | Consent Manager framework takes effect (Rule 4) | Weeks away |
| May 2027 | Core obligations take effect: notice, security safeguards, breach intimation, retention, children’s data, rights and grievance redressal (Rules 3 and 5 to 16) | Still ahead |
In early 2026, MeitY consulted stakeholders on shortening the transition window for Significant Data Fiduciaries from eighteen to twelve months. Institutions should track official notifications on the MeitY website rather than plan around the latest possible date. The framing from the session was direct: this was never a 2027 problem. The 18-month implementation window runs from 13 November 2025 to 13 May 2027. Readiness takes quarters, not weeks, and as of late 2026, almost two-thirds of the transition period has already passed.
The Consent Continuity Gap: why a checkbox is not compliance
The Consent Continuity Gap is the distance between the consent an institution collects at the point of entry and the processing that actually happens downstream. A student ticks a box on an application form. That data then travels into the CRM, the ERP, the LMS, marketing tools, a scholarship partner and a hostel system. If the consent, its purpose and its scope do not travel with the data, the institution can no longer show that each use is covered.
The DPDP Act sets a high bar for consent. Section 6 requires it to be free, specific, informed, unconditional and unambiguous, given through a clear affirmative action, and limited to the specified purpose. It also requires withdrawal to be as easy as giving consent. Meeting that bar once, at the form, is the easy part. The session framed the harder questions as two sets.
Validate and manage consent
- Is the consent free, specific and informed, with a clearly defined purpose and scope?
- Can you prove what was consented to, when, where and for what purpose, through a record that cannot be altered?
- For students under 18, can you verify the parent or guardian and link their consent to the student’s data and journey?
- Can you handle updates, renewals and withdrawals across the full student lifecycle?
Carry consent through the data journey
- Upstream: is the right consent, purpose and scope captured across admissions, applications, portals and counselor-assisted journeys?
- Downstream: does consent follow the data into ERP, CRM, LMS, marketing platforms and internal teams?
- Third parties: do vendors and processors follow the same purpose and permissions?
- When consent changes: does a withdrawal propagate across connected systems, adjusting access or stopping processing?
Closing the Consent Continuity Gap is what separates an institution that collected consent from one that can prove it is acting on it.
The seven proofs of DPDP readiness
A useful way to read the DPDP Act is to ask, for each obligation, what evidence the institution could put on the table if the Data Protection Board, an auditor or a parent asked. We call these the Seven Proofs of DPDP Readiness. Each one pairs what the law requires with what readiness looks like on a campus.
Proof 1: A complete data map
Every other DPDP control depends on knowing what personal data the institution holds, where it goes and why. Without a map, notices cannot be accurate, retention cannot be scheduled and a breach cannot be scoped.
A readiness review should be able to answer yes to eight questions:
- Collection: Is every collection point identified, including webforms, admission portals, CRM, offline forms and APIs?
- Data Principals: Is every group listed, including students, applicants, parents, staff and vendors?
- Systems: Is every system that stores or processes personal data documented?
- Data flows: Can you trace how data moves between admissions, finance, academics and marketing?
- Third-party sharing: Is there a current list of every third party that receives or processes personal data?
- Storage locations: Is it known where all data sits, across cloud platforms, internal servers and SaaS tools?
- Processing grounds: Is the lawful ground, consent or a legitimate use, identified for each data category?
- Retention and deletion: Is there a defined retention period and deletion process for each category?
Evidence to hold: a living record of processing activities, owned by a named person and reviewed on a schedule.
Proof 2: A privacy notice that stands on its own
Section 5 of the Act and Rule 3 of the DPDP Rules require a notice that accompanies or precedes every request for consent. Drawing on Rule 3, the session set out six tests for a compliant notice:
- Stand on its own: readable independently, not buried in terms of service
- Itemize the data: each item of personal data and the specific purpose for it
- Explain withdrawal: how to withdraw consent, as easily as it was given
- Explain rights: how to exercise rights and how to complain to the Data Protection Board
- Name a contact: a grievance officer or Data Protection Officer, with a working link
- Speak their language: available in English or any of the 22 languages in the Eighth Schedule to the Constitution
One point institutions often miss: Section 5(2) also covers personal data collected on the basis of consent given before the Act came into force. Existing applicant and alumni databases are in scope, and those Data Principals must receive a notice as soon as reasonably practicable.
Evidence to hold: versioned notices per collection point, with a record of which notice each Data Principal saw.
Proof 3: Valid, verifiable consent, including for students under 18
The DPDP Act defines a child as anyone under 18. Section 9(1) requires verifiable consent from a parent or lawful guardian before processing a child’s personal data, and Section 9(3) prohibits tracking, behavioral monitoring and targeted advertising directed at children. Rule 10 describes how verification can work, including reliable identity details already held, details provided by the parent, or a virtual token from an authorized entity such as a DigiLocker service provider.
This matters for higher education more than it first appears. Many applicants for undergraduate programs are 16 or 17 when they first enquire, which means admissions outreach to them falls under the children’s provisions.
Section 9(4) allows the Central Government to exempt certain classes of Data Fiduciaries, or certain purposes, from these requirements. The DPDP Rules, 2025 use this power in Rule 12 and the Fourth Schedule. For educational institutions, the exemption is narrow: it covers tracking and behavioral monitoring only to the extent needed for the institution’s educational activities, or in the interest of the safety of children enrolled with it. Separately, Part B of the Fourth Schedule permits purposes such as determining a child’s real-time location for their safety.
The exemption is bounded by purpose and applies to enrolled students. It does not extend to commercial profiling or targeted advertising directed at children, which remain prohibited. Marketing outreach to prospective applicants under 18 generally falls outside the exemption, so it requires verifiable parental consent. Institutions should confirm their specific position with legal counsel against the final notified text.
Evidence to hold: an immutable consent record for each Data Principal, linked to purpose, and a parental verification record for every applicant or student under 18.
Proof 4: Rights requests answered on time
Sections 11 to 14 of the Act give every Data Principal five rights:
| Right | What the individual can ask for |
| Right to information | Confirmation of processing, a summary of the personal data and processing, and the identities of other Data Fiduciaries with whom it was shared. |
| Right to correction | Correction of inaccurate data, completion of incomplete data, or an update. |
| Right to erasure | Erasure where the data is no longer needed for the specified purpose, unless retention is required by law. |
| Right to grievance redressal | A readily available grievance mechanism. Under Rule 14, the institution must publish a response period of no more than 30 days (or the specific period prescribed for your category of Data Fiduciary). |
| Right to nominate | Nomination of one or more individuals to exercise rights in the event of death or incapacity. |
For a university, a single request can touch admissions, examination, finance and alumni systems at once. Without the data map from Proof 1, a 90-day window shrinks quickly.
Evidence to hold: a rights request log showing receipt date, systems searched, action taken and closure date.
Proof 5: A retention schedule that actually deletes
Section 8(7) requires a Data Fiduciary to erase personal data once the specified purpose is no longer served, unless the law requires longer retention. Clarify that 1-year log retention applies specifically to security, traffic, and processing logs under Rule 8 and cyber-security directives, rather than general student personal records.
Retention in a university is not one number. It should be linked to the purpose of each category:
| Data category | Retention should be linked to |
| Application data | Admission process plus applicable legal and grievance requirements |
| Applicant documents | Verification plus applicable requirements |
| Counseling records | Admission process plus grievance handling |
| Communication records | Communication purpose plus applicable requirements |
| Payment records | Financial and tax requirements |
| Consent records | Demonstrating and managing consent |
| Security and processing logs | DPDP requirements plus security needs |
The test the session posed is worth repeating: is there a written schedule for each category, and is deletion actually running, including in backups and vendor systems?
Evidence to hold: an approved retention schedule and deletion logs that show it being applied.
Proof 6: Security safeguards you can demonstrate, including at your vendors
Section 8(5) requires a Data Fiduciary to take reasonable security safeguards to prevent a personal data breach. Failure to do so carries the highest penalty in the Act: up to ₹250 crore. Rule 6(1) sets out the minimum measures:
- Data protection: encryption, obfuscation, masking or the use of virtual tokens mapped to personal data
- Access control: appropriate measures to control access to the computer resources used for processing
- Visibility of access: logs, monitoring and review to detect unauthorized access, investigate it and prevent it from happening again
- Continuity: measures such as data backups so that processing can continue if confidentiality, integrity or availability is compromised
- Log retention: logs and personal data kept for at least one year to help detect unauthorized access and support investigation, unless another law requires otherwise
- Processor contracts: provisions in contracts with Data Processors requiring them to take reasonable security safeguards
- Organizational measures: appropriate technical and organizational measures to make sure the safeguards are actually observed
Beyond this minimum, good practice includes role-based, least-privilege access and periodic vulnerability assessment and penetration testing based on risk.
The last item is where many institutions are most exposed. A university may run admissions on a CRM, learning on an LMS and fees on a payment platform, and each one is a Data Processor acting on its behalf. The institution remains accountable for all of them.
Evidence to hold: documented controls for every system holding personal data, recent test reports, and processor contracts with security, deletion and confidentiality clauses.
Proof 7: A breach protocol your staff can run
Under Section 8(6) and Rule 7, the clock starts the moment the institution becomes aware of a personal data breach. The protocol discussed in the session runs in five steps:
- Detect: identify the incident.
- Escalate: trigger internal escalation and an impact assessment.
- Intimate without delay: inform the Data Protection Board and every affected Data Principal.
- Report within 72 hours: submit a detailed report to the Data Protection Board, unless the Board allows a longer period on written request.
- Review: run a post-incident review and fix the controls that failed.
Failing to notify the Board and affected Data Principals can attract a penalty of up to ₹200 crore.
The session’s most practical point was about people. Most breaches start with a person, not a system. A breach need not be a sophisticated cyberattack. It can be an applicant list sent to the wrong institution, an exposed counseling sheet, an unauthorized lead export or a document shared with the wrong person. Training therefore has to reach every team that touches student data, including admissions, faculty, finance, hostel and IT, and cover consent capture, safe sharing without personal messaging apps or personal drives, rights requests, and how to recognize and report a breach.
Evidence to hold: a written breach playbook with named owners, breach drill records and training attendance kept as evidence.
Policy-level compliance vs practice-level readiness
| Area | Policy-level compliance | Practice-level readiness |
| Data inventory | A one-time spreadsheet | A living data map with an owner and review cycle. |
| Notice | A privacy page linked in the footer | Must be a standalone document presented prior to or at the time of collecting consent, independent of general terms and conditions. |
| Consent | A checkbox on the application form | Purpose-linked consent records that travel to every system. |
| Children | An age field on the form | Verified parental consent linked to the student record. |
| Rights | An email address for requests | A tracked workflow with a published response period. |
| Retention | A clause saying data is kept “as long as necessary” | Category-wise schedules with deletion logs, including at vendors. |
| Security | A security policy document | Tested controls and processor contracts that require them. |
| Breach | An incident policy | A rehearsed protocol that meets the 72-hour report. |
What DPDP penalties apply to universities?
The Schedule to the DPDP Act, 2023 sets the maximum penalty for each type of breach. The Data Protection Board decides the actual amount based on factors such as the nature, gravity and duration of the breach.
| Breach | Maximum penalty |
| Failure to take reasonable security safeguards (Section 8(5)) | Up to ₹250 crore |
| Failure to notify the Board and affected Data Principals of a personal data breach (Section 8(6)) | Up to ₹200 crore |
| Non-fulfillment of obligations in relation to children (Section 9) | Up to ₹200 crore |
| Non-fulfillment of additional obligations of a Significant Data Fiduciary (Section 10) | Up to ₹150 crore |
| Breach of any other provision of the Act or the Rules | Up to ₹50 crore |
For most institutions, the larger cost is trust. Students and parents share their data at a moment of high stakes, and how an institution handles that data increasingly shapes how it is perceived.
A quarter-by-quarter DPDP readiness plan for universities
With the core obligations applying from 13 May 2027, the 18-month transition window (13 November 2025 to 13 May 2027) provides a structured runway to move from policy to practice.
A practical sequence across the transition window looks like this:
| Phase | Window | Focus | Key actions |
| Phase 1 | November 2025 – June 2026 | Govern and map | Name an accountable owner and a grievance contact. Build the data map across all collection points, systems, and vendors. Identify the processing ground for each data category. Run a gap assessment against the Seven Proofs. |
| Phase 2 | July 2026 – December 2026 | Notice and consent | Redesign notices as standalone documents for every collection point, in the languages your applicants use. Rebuild consent capture with purpose-level records. Set up parental verification for applicants under 18. Plan notices for legacy databases under Section 5(2). Review and amend processor contracts. |
| Phase 3 | January 2027 – May 2027 | Operate and prove | Publish the rights and grievance process with its response period. Approve the retention schedule and switch on deletion, including at vendors. Test security controls. Run a breach drill against the 72-hour clock. Train every team that touches student data. Assemble the evidence pack before the 13 May 2027 deadline. |
The order matters. Notices written before the data map is complete tend to be inaccurate, and retention schedules set before purposes are defined tend to be arbitrary.
Five questions for your governing body
For leaders who want a short test of where the institution stands, these five questions summarize the session.
- Can we list every system and vendor that holds student personal data today?
- Can we show the consent and notice behind any one student’s data, in every system it sits in?
- Do we verify parental consent for applicants under 18, and can we prove it?
- Is deletion running on a schedule, including in backups and vendor systems?
- If a breach were discovered this afternoon, who would file the report to the Data Protection Board within 72 hours?
If any answer is uncertain, that is where readiness work should begin.
Where technology fits in DPDP readiness
Technology does not make an institution compliant on its own, but it decides whether compliance can be sustained at scale. Two capabilities came up repeatedly in the session.
Consent infrastructure. Purpose-level consent notices, multilingual delivery, consent receipts and a dashboard where Data Principals can review or withdraw consent are what close the Consent Continuity Gap in practice.
Processor discipline. Because the institution stays accountable for its vendors, the platforms that hold admissions and student data must themselves be built for DPDP. Meritto, the AI-powered Operating System for Student Enrollments from NoPaperForms Solutions Limited, acts as a Data Processor for the educational institutions it serves. Its approach, presented in the session as Meritto Secure, covers:
- Security controls: an ISO/IEC 27001 aligned information security management system, SOC 2 Type II controls, encryption, masking, data isolation, disaster recovery and a high-availability architecture
- Access governance: role-based access control, MFA and SSO, IP restrictions and least-privilege enforcement
- Auditability: audit logs covering logins, data access, exports and system activity
- Processor discipline: processing limited to institutional instructions, controlled sub-processors, and contract-backed obligations for security, deletion and confidentiality
- Privacy by design: platform capabilities that support data minimization, retention control and secure deletion aligned with institutional policy
When evaluating any vendor, institutions can apply the same Seven Proofs: ask each processor what evidence it can produce for the controls it operates on your behalf.
From policy to proof: what universities should do next
Most universities already have a privacy policy. Under the DPDP Act, that is not enough. The Data Protection Board, an auditor or a parent can ask an institution to show how student data is actually handled: what was collected, what consent was given, who accessed it and when it will be deleted. A policy cannot answer those questions. Records, processes and systems can.
That is the shift from policy to proof. With core obligations applying from May 2027, the coming months are the time to map student data, fix notices and consent, set retention schedules, review vendor contracts and rehearse breach response. Institutions that start now will meet the deadline with less disruption and can answer students and parents with confidence when they ask how their information is protected.
Watch the full session here
About Meritto
Meritto is the AI-powered Operating System for Student Enrollments and NoPaperForms’ flagship product for student enrollments. It is a unified, modular and automated platform purpose-built for educational organisations, enabling them to attract, engage and enroll students on one platform.
By bringing data, context and workflows together, Meritto manages the complete enquiry-to-enrollment journey, from enquiry capture and student engagement to applications, document verification, admission offers and final enrollment. It serves as the system of record for the enrollment journey, helping educational organisations grow enrollments, improve conversions, optimise marketing spends and increase operational efficiency.
About Collexo
Collexo is NoPaperForms’ Operating System for Fee Collections and Payments and its embedded payments platform, purpose-built for educational organisations.
It enables institutions to collect, manage, reconcile and report student-related payments through one unified platform, serving as the financial system of record for fee collection and payment workflows. Collexo integrates with licensed payment partners and payment gateways, while providing the software and technology layer required to manage education-specific fee collection and payment workflows.
About Mio AI:
Mio AI is NoPaperForms’ agentic AI platform and intelligence layer across its education technology platform. Built on the education-specific data, context and workflows of Meritto and Collexo, Mio AI enables educational organisations to deploy intelligent, goal-driven agents across student-facing and institutional workflows.
Mio AI Guide is a conversational AI agent for student-facing engagement. It can answer student queries in real time, capture and qualify enquiries, and guide students towards relevant next steps across defined enrollment journeys.
Mio AI Voice enables AI-led voice engagement across defined student journeys at scale, including qualification, reactivation and other enrollment workflows. Because Mio AI works with the underlying education context, its agents can use information such as a student’s stage in the enrollment journey, prior interactions and relevant next steps to make engagement more contextual and goal-driven.
About #illuminateByMeritto:
#illuminateByMeritto is Meritto’s product webinar series designed to bring you closer to what we’re building and how it works in real scenarios. From new feature launches to deep dives into workflows, each session focuses on helping teams understand, adopt, and get more value from the platform.
Built for our growing B2B community of 50,000+ education professionals, these sessions are designed to simplify complexity, showcase practical use cases, and help you drive more effective student engagement and enrollment outcomes.
FAQs: DPDP Readiness for Higher Education
Yes. Any university, college or institute that processes digital personal data of applicants, students, parents or staff is a Data Fiduciary under the DPDP Act, 2023. This applies to public and private institutions, and to data collected online or collected offline and later digitized.
Most obligations apply from May 2027, eighteen months after the DPDP Rules were notified on 13 November 2025. These include notice, security safeguards, breach intimation, retention, children’s data, and rights and grievance redressal. The Consent Manager framework applies from November 2026.
Yes, in most cases. Section 9(1) of the DPDP Act requires verifiable parental consent before processing the personal data of anyone under 18. Under Section 9(4), the DPDP Rules exempt educational institutions only for tracking and behavioural monitoring needed for educational activities or the safety of enrolled students. Commercial profiling and targeted advertising directed at children remain prohibited, and marketing outreach to prospective applicants under 18 requires verifiable parental consent.
The vendor is a Data Processor and must follow the institution’s instructions and contractual safeguards. However, the university as Data Fiduciary remains accountable for compliance under Section 8(1), including for processing its vendors carry out on its behalf.
The institution must inform the Data Protection Board and every affected Data Principal without delay once it becomes aware of a breach. It must then submit a detailed report to the Board within 72 hours under Rule 7, unless the Board allows more time on written request.
Only as long as needed for the specified purpose, unless another law requires longer retention. Each data category, such as applications, payments or counselling records, should have its own retention period. Processing logs must be kept for at least one year under Rule 8.
Under the Schedule to the DPDP Act, 2023, penalties go up to ₹250 crore for failing to take reasonable security safeguards, up to ₹200 crore for failing to notify the Board and affected Data Principals of a breach, up to ₹200 crore for not meeting obligations in relation to children, up to ₹150 crore for not meeting the additional obligations of a Significant Data Fiduciary, and up to ₹50 crore for breach of any other provision. The Data Protection Board decides the amount based on the nature, gravity and duration of the breach.
The Consent Continuity Gap is the distance between the consent an institution collects at the point of entry and the processing that happens downstream. It is closed when consent, purpose and scope travel with the data into every system and vendor that uses it.
Recommended Reads
- DPDP compliance for higher education: How universities move from policy to institutional practice

- The new growth playbook for higher education
- How Mio AI Voice helps institutions achieve enrollment outcomes at scale
- Connected Intelligence: The Infrastructure Behind Institutional Agility
- More Data, But Less Insight? Inside the Intelligence Era of Education
- How universities can turn AI into real institutional impact